Case study/Product engineering/Cybersecurity
WeHackU
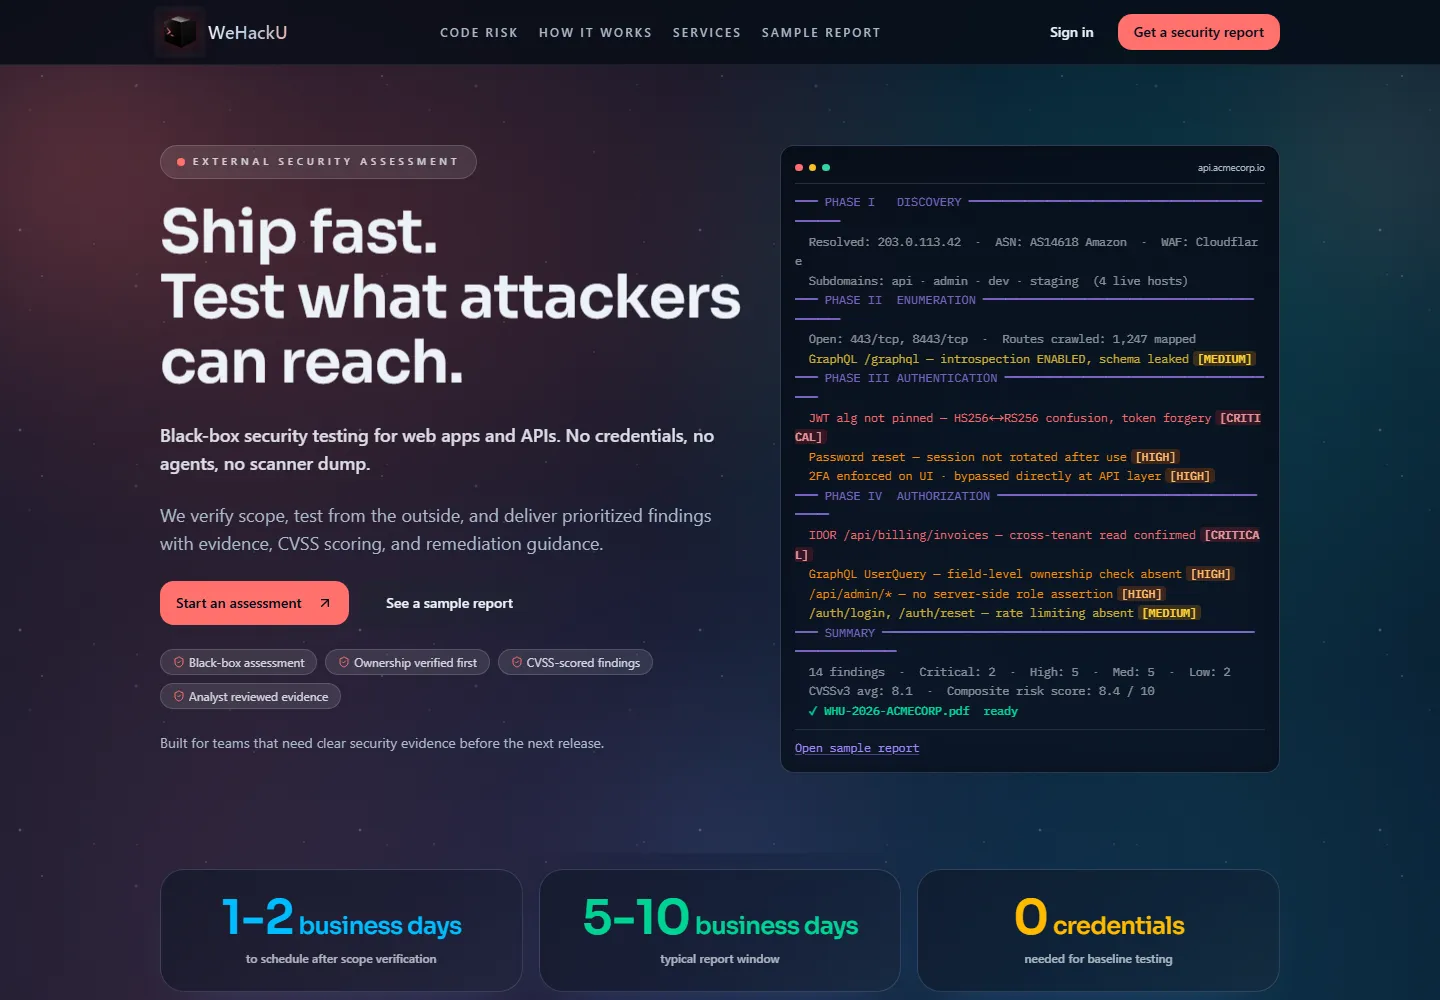
Security testing for web apps and APIs, from the outside. Every finding comes with evidence, its impact, and a clear fix.
- Role
- Product engineering
- Service
- Black-box testing
- Starts
- Within 1–2 business days
- Report
- Usually 5–10 business days
(01) The idea
Teams that ship quickly still need to know what an attacker could reach. Scanner output rarely says which issues matter.
WeHackU tests from the outside, the way an attacker would, and turns what it finds into something a team can act on.
(02) What it does
-
Prioritised findings
Grouped by risk and scored with CVSS.
-
Reproducible evidence
The requests and responses behind each finding.
-
Business impact
What each issue could mean for the team.
-
Clear fixes
Suggested remediation, with an optional retest.
-
A broad baseline
Authentication, access control, APIs, IDOR, SSRF, uploads, and rate limits.
-
No access needed
No credentials, VPN, or agents to set up.
(03) How an assessment runs
-
01
Define the target
Name the app or API in scope.
-
02
Verify ownership
A token on the domain confirms it.
-
03
Test from outside
Non-destructive, within the approved scope.
-
04
Receive the report
Findings, evidence, impact, and fixes.
(04) Choices
- 01
Verify first
Nothing is tested until ownership is confirmed.
- 02
Safe by default
Testing stays non-destructive; anything heavier needs written approval.
- 03
People, not just scanners
An analyst validates every finding, which is how logic flaws get caught.
(05) Today
Taking new assessments at wehacku.com.
Visit wehacku.com